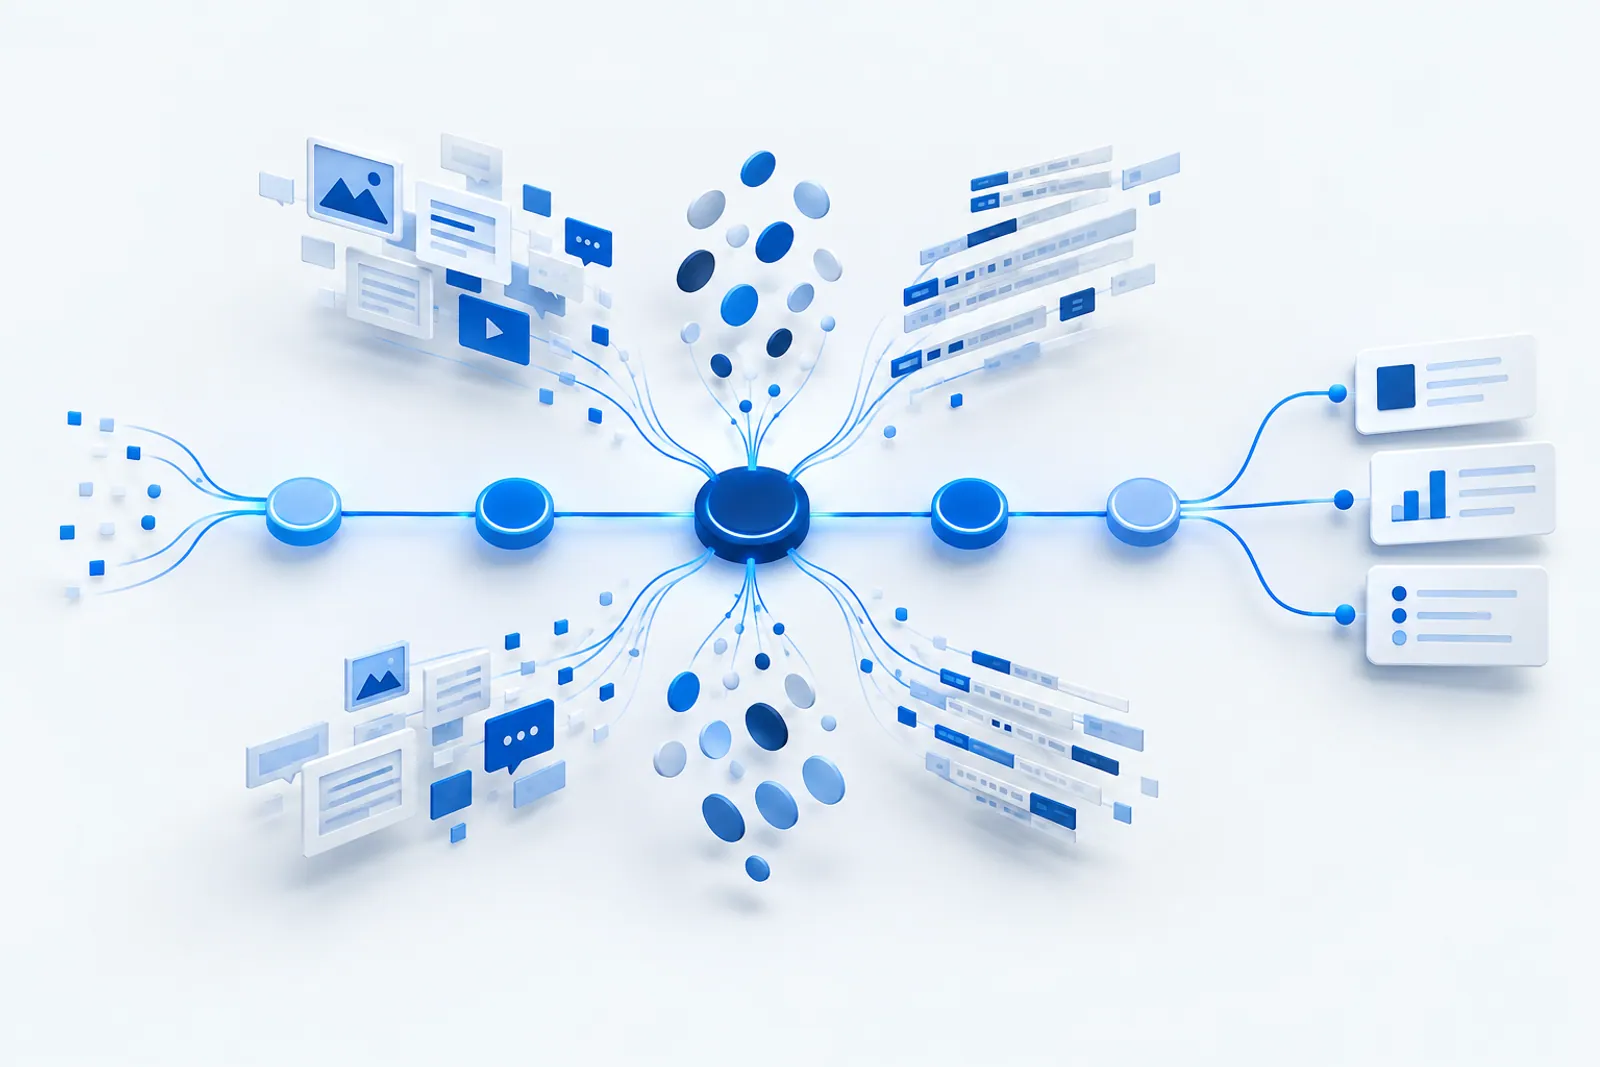
Seven engines connect monitoring signals
Xingju Tianshu Security Operations Center monitors websites and public digital assets for content compliance and intrusion signals. It cross-checks page content, visual changes, browser behavior, access identities and regional egress, connecting detection with human confirmation and rule operations.
Website monitoring must detect real anomalies while controlling false positives on normal pages. Tianshu cross-checks multiple signals across websites and public digital assets, connecting detection, human confirmation, feedback and rule operations.
Defacement signatures
Identify defacement signatures without historical baselines, including sites with existing anomalies.
Sensitive-content detection
Provide five-category scoring, variant decoding, allowlists and feedback; outcomes depend on lexicon coverage, updates and customer-specific operation.
Visual-change detection
Combine full-page capture, perceptual hashes and pixel differences to identify visual anomalies despite similar text.
Multi-view rendering
Compare distribution across ten perspectives, including desktop, mobile, search crawlers, AI crawlers and no-JavaScript rendering.
Runtime behavior analysis
Observe dynamic injection, encoded execution, delayed callbacks, redirects and internal-network probing signals in a browser sandbox.
AI input-surface security
Check hidden elements, HTML comments, attributes, zero-width text and encoded payloads for prompt injection. AI assistance does not decide final alerts.
Distributed perspectives
Cross-check multiple cloud nodes for anomalous content targeted by region or egress IP.
Operate content compliance
The content-compliance engine framework is available, while its lexicons still require continued development and operation. Use results with customer-specific context, human confirmation and feedback.
Evaluation results with explicit boundaries
The release also discloses early findings: initial detection was 12.9% across 70 defaced pages, while all 11 normal sites initially triggered alerts. Iterations addressed real samples, exclusion rules and false positives; both historical and later results are limited to their respective versions and samples.
The company release reports results for its stated version and internal samples: 95.7% detection across 70 archived defaced pages; 0.0% sample false positives across 11 normal sites and 41 normal pages; and 51 passes, four partially available results and zero failures across 55 end-to-end checks.
These are the release article’s internal evaluation results, not universal accuracy or SLA commitments. Reported remaining misses mainly involve replaced GIF and JPG image files; additional image-content comparison is planned.
For web inputs to AI and private environments
Supports private deployment with encrypted cloud and model credentials. Domestic or local model interfaces can retain data within the customer network. External YAML rules support hot reload, with YARA integration; confirm model interfaces and node scope for the deployment environment.