Identity & Least Privilege
Use dedicated identities, short-lived credentials and granular authorization.
Control autonomous tool use through agent identity, least privilege, instruction isolation, allowlists, human approval and complete action audit.
Agents misinterpret tasks and invoke privileged tools or destructive actions
Malicious instructions in external content hijack agent decisions
Long-lived identities and credentials violate least privilege
Multi-agent workflows lack accountability, approvals and action replay
Use dedicated identities, short-lived credentials and granular authorization.
Separate system instructions, user input and external content against indirect injection.
Enforce allowlists, parameter validation, risk tiers and human approval.
Record plans, tool calls and results to detect and investigate abnormal chains.
Identify agents, tools and responsible actors.
Check permissions, parameters and action risks.
Allow, request approval or block according to policy.
Connect call chains, execution results and audit records.
Scope, schedule and acceptance criteria are agreed following assessment.
Discuss this approach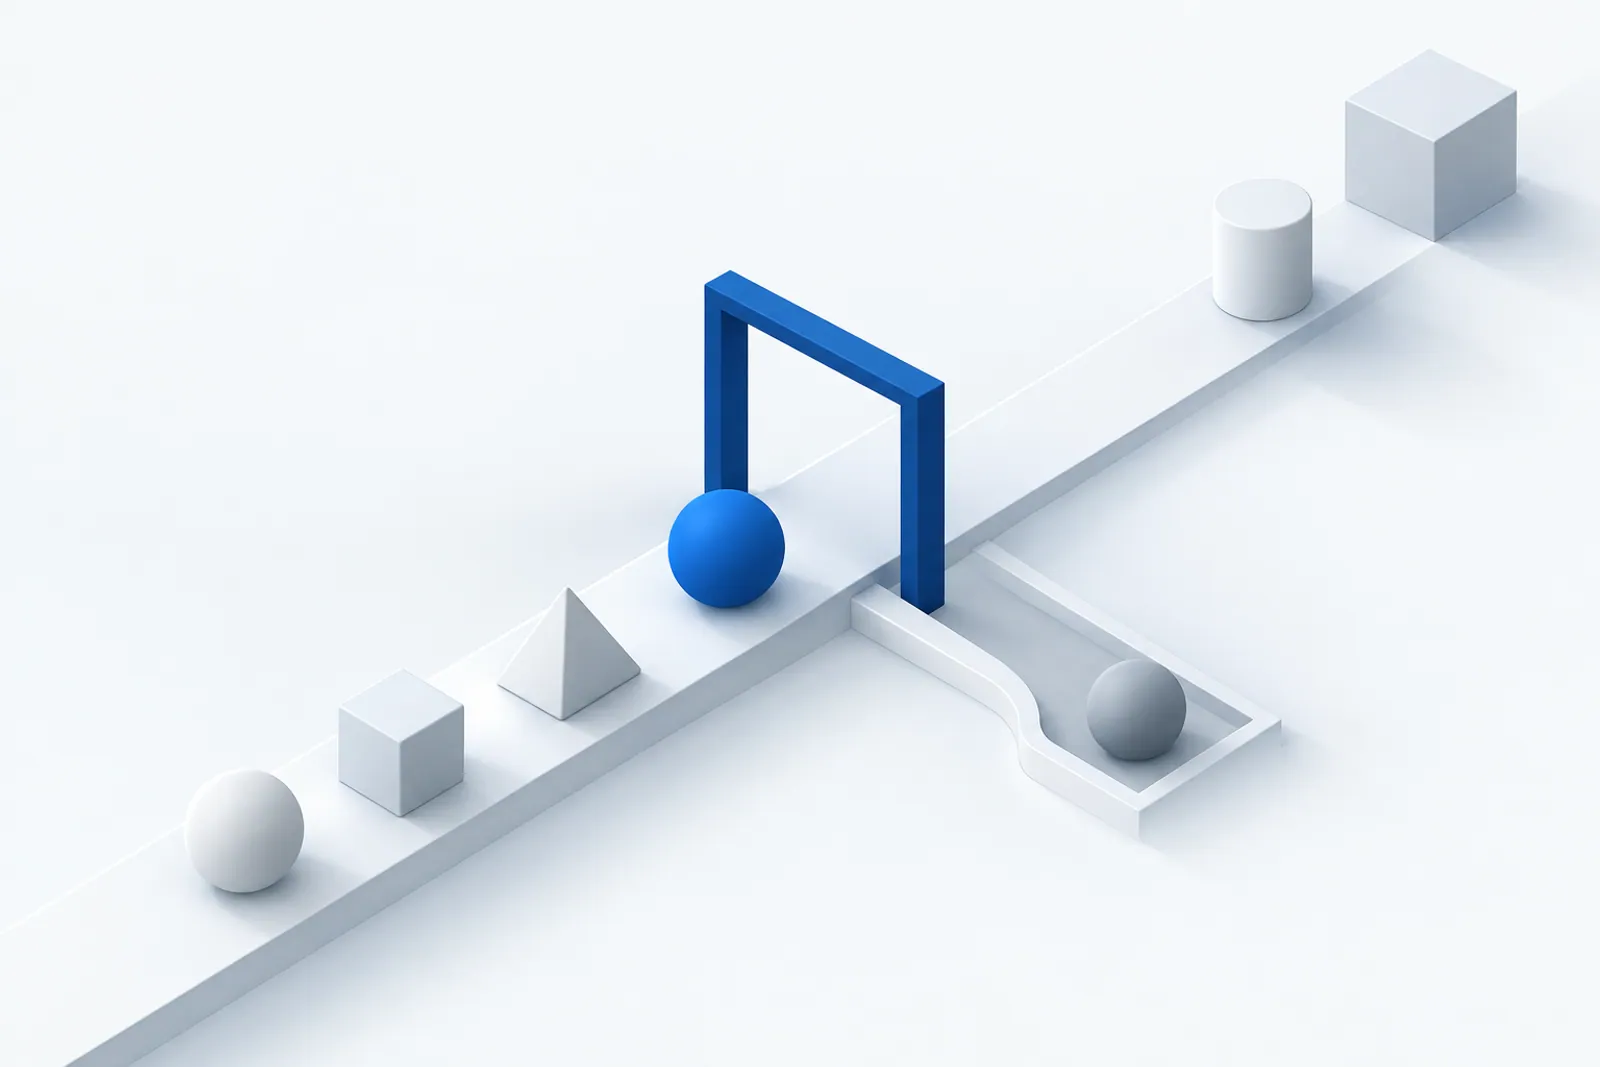
Every Agent action passes a security gate before execution
A unified security control point for prompt-injection defense, input/output inspection, sensitive-data protection, access control and model-call audit.
Lifecycle security for LLM, AIGC, RAG and agent applications across data, model, application and operations layers.