Multimodal Risk Detection
Detect text, image and contextual risks with optional local hard constraints.
An operational loop for multimodal risk detection, policy decisions, human review, sample feedback and audit across generated content.
Generated content creates regulatory, bias, discrimination or brand risk
Variants, euphemisms and multimodal inputs bypass moderation controls
Manual review cannot match real-time dialogue and content scale
Policy, review, appeal and sample feedback remain disconnected
Detect text, image and contextual risks with optional local hard constraints.
Configure allow, block, replace or review actions by business and risk level.
Support review, sampling, appeals, label correction and quality evaluation.
Use standard APIs or compatible gateways for unified input and output checks.
Define content types and review entry points.
Apply content policies to detection results.
Connect human review, feedback and exception handling.
Retain review outcomes to inform policy improvements.
Scope, schedule and acceptance criteria are agreed following assessment.
Discuss this approach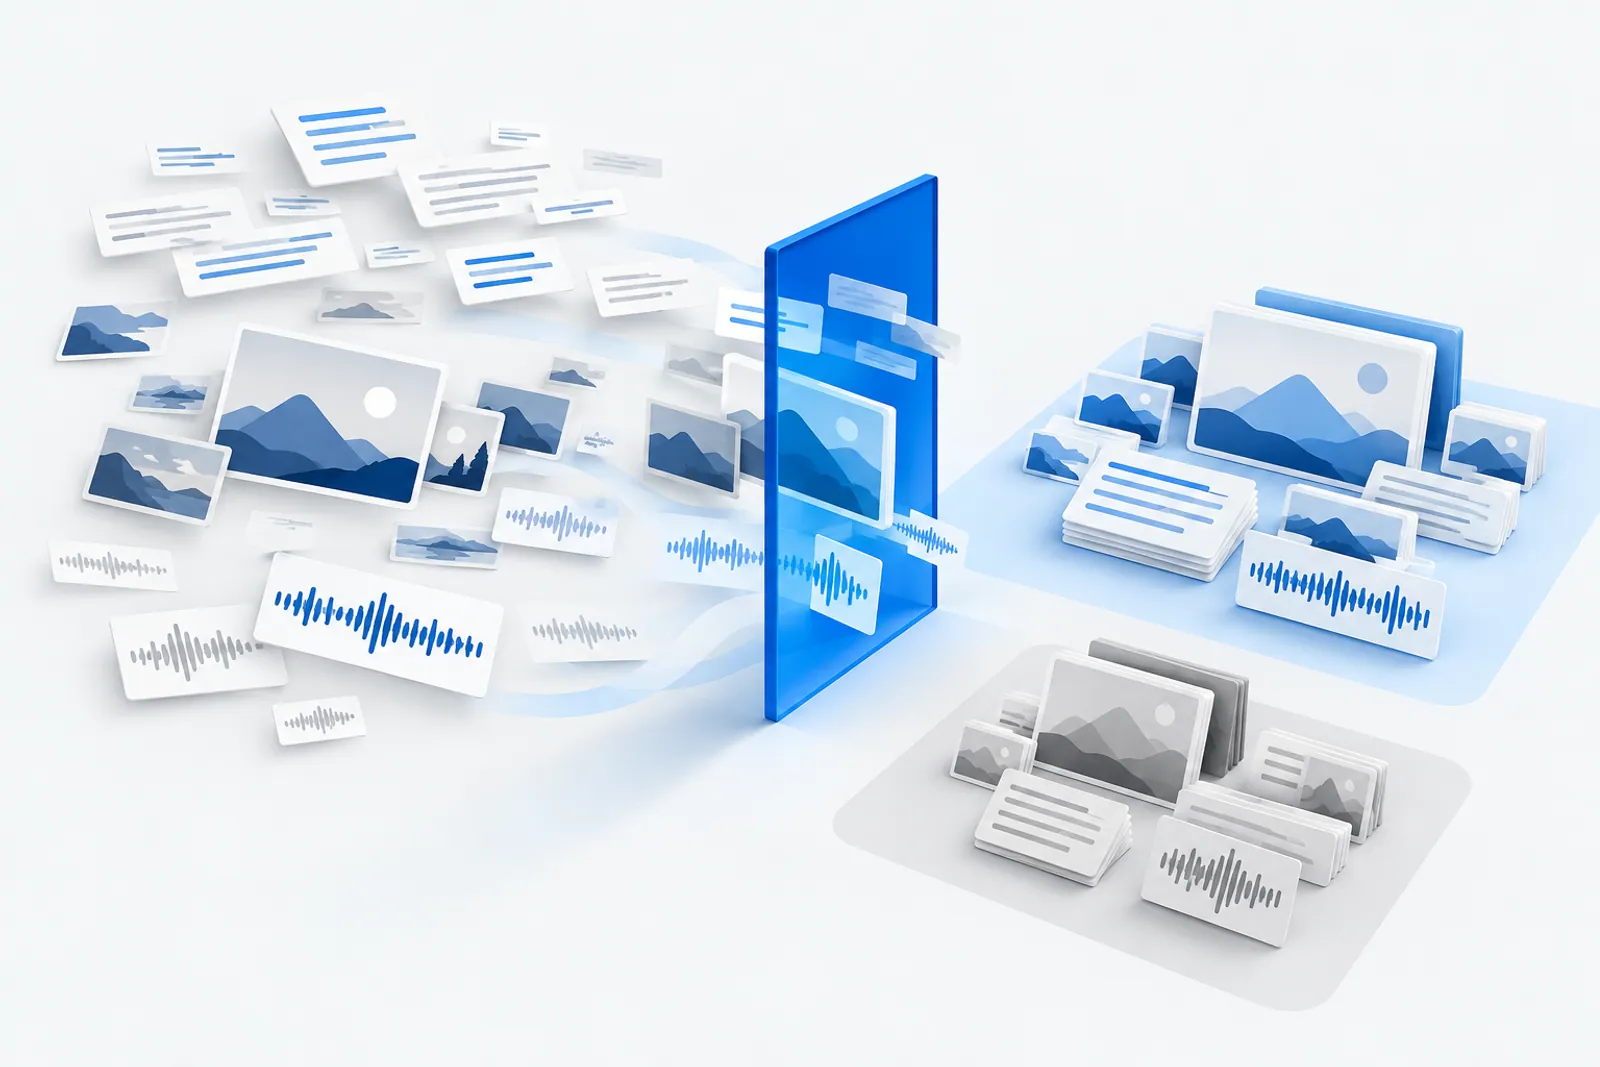
Connect content review, policy decisions and ongoing operations
A unified security control point for prompt-injection defense, input/output inspection, sensitive-data protection, access control and model-call audit.
Lifecycle security for LLM, AIGC, RAG and agent applications across data, model, application and operations layers.